Your business, protected 24/7
Security experts watching your devices, Microsoft 365 accounts and network around the clock, and ready to act within minutes when something looks wrong.
- 24/7 SOC
- 8-minute average response
- Works with Microsoft Defender
The threat has changed
What are attackers doing differently to businesses like yours?
Stolen login sessions
Microsoft 365 sessions copied and reused from overseas, getting past passwords and multi-factor authentication.
Compromised accounts
Convincing phishing emails that trick staff into handing over access to email and files.
Malicious websites
Staff directed to sites linked to ransomware groups, often from a single click.
In every case, the attacker is trying to get in quietly and stay unnoticed.
The pace has accelerated
Attackers now use AI to find weak spots, write convincing phishing emails and build working attacks.
We expect this pace to keep increasing over the next two years.
What the NCSC says
The UK's National Cyber Security Centre is clear about the direction of travel.
“Increase the speed, scale and efficiency”
“A race to shorten patch deployment timelines”
Source: NCSC Annual Review 2026, “The impact of AI on cyber threat”, ncsc.gov.uk
- Sun 03:12Suspicious Microsoft 365 sign-in from overseas detected
- 03:14SOC analyst confirms a stolen login session
- 03:20Account locked and the attacker signed out
- 08:30Everon calls you to reset the password
Antivirus alone is no longer enough
Antivirus and good passwords are still essential, but on their own they no longer stop modern attacks. What makes the difference now is having security experts watching for the signs of an attack around the clock, and able to act within minutes.
- 24/7 monitoring, including 3am on a Sunday
- Response in minutes, not the next working day
- Part of our standard security baseline on every managed support plan
Protection in layers
Three fully managed services that together cover your devices, your identities and your network.
Managed EDR
Protects your computers and servers
Spots hacker behaviour antivirus misses, such as hidden footholds, ransomware activity and attackers moving between machines, and isolates the device fast.
Managed ITDR
Protects your Microsoft 365 accounts
Watches sign-ins for stolen passwords, hijacked sessions and suspicious mailbox rules, and can lock an account and sign the attacker out immediately.
Managed SIEM
Monitors your firewall and network
Collects security logs from your firewall and key servers so suspicious activity across the network is spotted. Added where your firewall is compatible.
All prices exclude VAT.
Catching what antivirus misses
Fully managed, enterprise-grade endpoint detection and response, built for small and medium businesses.
Persistent footholds
Finds and removes threats hiding in plain sight on Windows and macOS.
Malicious process behaviour
Behavioural analysis that identifies and stops suspicious hacker activity.
Ransomware canaries
Early-warning tripwires that catch potential ransomware incidents early.
Lateral movement
Detects attackers trying to spread from one machine to the next.
External recon
Highlights exposed entry points so your attack surface can be reduced.
Threat response
From immediate containment to remediation and guided recovery, at every step.
Get more from your Microsoft security
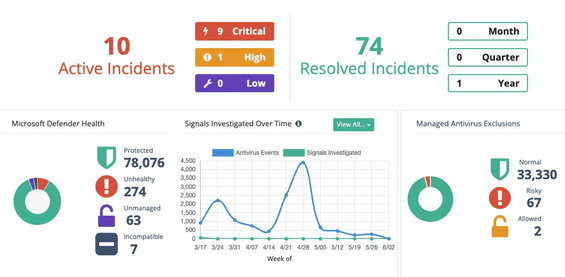
Huntress is a strategic Microsoft partner. It works with the Microsoft Defender you already have, rather than replacing it, so you get more from what you already pay for.
Microsoft Defender Antivirus + Managed EDR
Defender Antivirus is centrally managed and optimised at no extra cost: configurations, exclusions, scans and remediation, all looked after for you. You get more from a tool you already have, and your budget goes where it matters.
Microsoft Defender for Endpoint + Managed EDR
If you use Defender for Endpoint, its critical and high-severity alerts are investigated by the 24/7 SOC as an extra source of detection. Noise and false positives are filtered out, so you only hear about confirmed threats.
Microsoft 365 + Managed ITDR
Built for Microsoft 365 and Entra ID. Analysts watch for session hijacking, credential theft and rogue OAuth apps in real time, and act on Microsoft's risky-user signals to close weak spots.
Huntress by the numbers
Figures from Huntress datasheets.
Nothing. We've got it.
We deploy everything remotely. It runs quietly in the background, doesn't slow computers down, and your team won't notice any change to how they work.
If we ever need you to act, for example resetting a password after a suspicious sign-in, we’ll contact you straight away.
Easy to deploy, leverages Windows Defender so we get simplicity, extra feature set and management for the same overall cost as comparable antivirus.
Your questions, answered
Want to talk it through? We're happy to arrange a call.
Antivirus is still essential, but it looks for known bad files. Modern attacks often use stolen logins and legitimate tools, so there is nothing for antivirus to catch. Managed detection and response adds security experts watching for the behaviour of an attack around the clock, and acting on it within minutes.
EDR (endpoint detection and response) protects your computers and servers. ITDR (identity threat detection and response) protects your Microsoft 365 accounts and sign-ins. SIEM collects security logs from your firewall and key servers so activity across the network can be spotted. Together they cover devices, identities and the network.
No. Huntress works with the Microsoft Defender you already have rather than replacing it. It manages Defender centrally and acts on its alerts, so you get more from what you already pay for.
No. It runs quietly in the background and your team won't notice any change to how they work. We deploy everything remotely, with no disruption.
The Huntress SOC is staffed 24/7, including weekends and bank holidays. They can isolate an infected device, or lock an account and sign an attacker out, straight away. If we need you to do anything, such as reset a password after a suspicious sign-in, we'll contact you immediately.
No. The service is fully managed. Everon and the Huntress SOC handle the monitoring, investigation and response, and we explain anything you need to know in plain English.
Find out how protected you really are
Book a free 15-minute call and we'll talk through where your business stands and what 24/7 protection would look like for you.